Skip to content

Certificates. Deployments. Automation.

TLSPilot: TLS Certificate Management for Modern IT

  • TLSPilot is a powerful certificate lifecycle management solution. It helps organisations manage public and private certificates across applications, services, VPN connections and other systems.

See how TLSPilot works Download Community Edition (free)

The problems with certificates

Manage shorter certificate lifetimes with confidence

Public TLS certificates are becoming valid for shorter periods, while the number of certificates in use continues to grow. Manual tracking increases the risk of missed renewals, service interruptions and security gaps. TLSPilot provides reliable enterprise certificate management from one central service.

  • Obtain certificates from internal or external certificate authorities.
  • Validate domains and issue certificates without manual steps.
  • Use automated certificate deployment for connected target systems.
  • Apply certificate renewal automation before certificates expire.
  • Distribute renewed certificates securely across your infrastructure.
  1. 5 years60 months, until 1 April 2015
  2. 39 monthsfrom 1 April 2015
  3. 825 daysfrom 1 March 2018
  4. 398 daysfrom 1 September 2020
  5. 200 dayssince 15 March 2026
  6. 100 daysfrom 15 March 2027
  7. 47 daysfrom 15 March 2029
Today

The cost

Invalid certificates = downtime!

86%at least one outage in the last year
31%every quarter
10%every week

Source: industry surveys 2024/2025

Notorious cases of certificate problems:

An expired certificate in the core network left 25 million O2 customers without mobile data for almost a day.

O26 Dec 2018 - almost 23 h

Azure Storage HTTPS went dark worldwide. The renewed certificates existed. They were never deployed.

Microsoft Azure22 Feb 2013 - about 12 h

"The active certificate in Google Voice frontend systems inadvertently expired." Some VoIP calls failed to connect for 4 hours 22 minutes.

Google Voice15-16 Feb 2021 - 4 h 22 min

Country sites including de.linkedin.com and ch.linkedin.com served an expired TLS certificate. Browsers blocked them for about three hours.

LinkedIn30 Nov 2017 - about 3 h

An internal wildcard TLS certificate expired. Logins for Fortnite and the Epic Games Store failed for more than five hours.

Epic Games6 Apr 2021 - a little more than 5.5 h

We've determined that an authentication certificate has expired causing users to have issues using the service.

Microsoft Teams3 Feb 2020 - about 3 h

Playback died for about an hour after a TLS certificate expired.

Spotify19 Aug 2020 - about 1 h

And with that, TLSPilot comes into play TLSPilot One service for the complete certificate lifecycle

Obtain certificates automatically

TLSPilot supports public and private certificates and simplifies pki-management. Certificate requests, validation and issuance are coordinated centrally, reducing repetitive administrative work.

Deploy certificates to every target

After issuance or renewal, TLSPilot publishes certificates to the required systems. Deployment works with existing tools and secured credentials, without requiring agents on target systems.

Renew and distribute again

With proactive certificate renewal automation, TLSPilot helps prevent expired certificates and unexpected downtime. Notifications provide clear information when attention is required.

How TLSPilot helps

Obtain. Renew. Deploy.
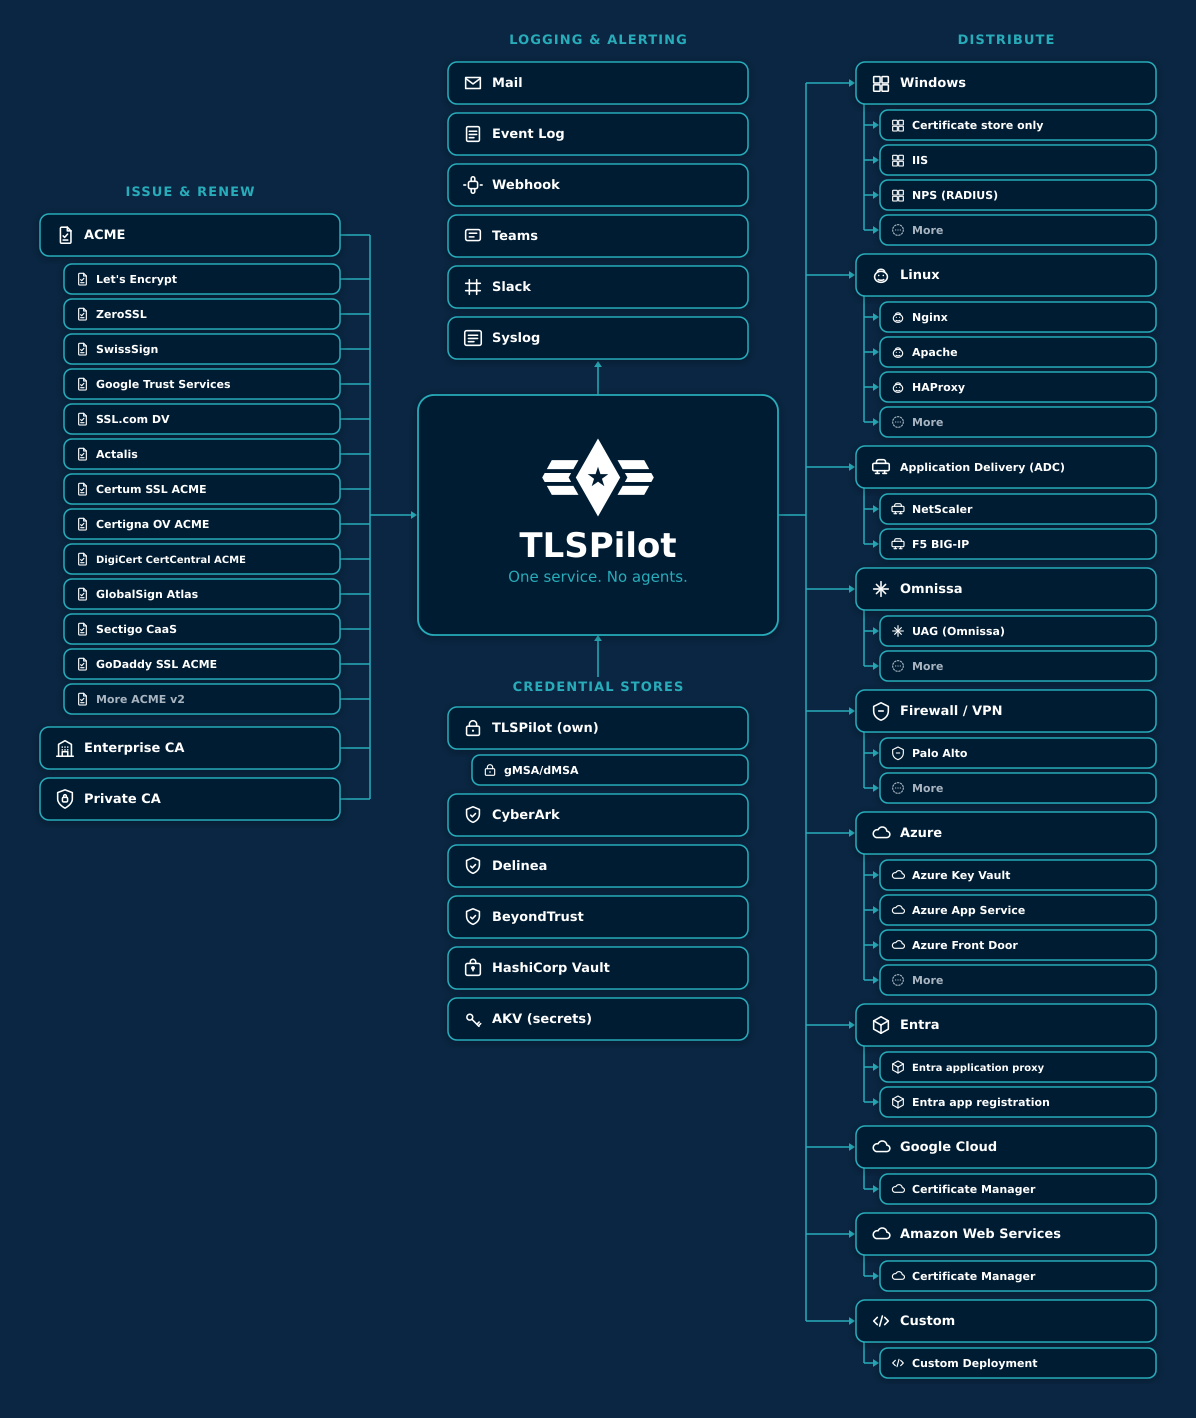
TLSPilot in the centre: left ACME with providers, Enterprise CA and Private CA; top Logging and Alerting; right distribute to Windows, Linux, ADC, Omnissa, Firewall/VPN, Azure, Entra, Google Cloud, AWS and custom script; bottom Credential Stores incl. gMSA

Certificate management for secure operations

Whether you need certificate management, certificate deployments, certificate expiry alerts etc. TLSPilot supports consistent processes for certificates across complex environments. Teams can also use the platform to renew TLS certificates efficiently and maintain transparent control of certificate status.

Reduce operational risk with CLM

TLSPilot combines issuance, deployment, renewal and monitoring in one structured CLM workflow: every 24 hours it checks for due renewals and missing deployments and reports them through the configured alert channels. This reduces manual effort, supports dependable service availability and gives IT teams a clear view of certificate operations.

Discover how TLSPilot can simplify certificate lifecycle management for your organisation.

See how TLSPilot works Compare editions

What counts as a certificate

Every configured certificate counts - internal or public. The cap is the stock on the host.

What counts as a deploy

Every configured deploy target counts. One certificate can serve several services - each target extra.

WebUI & RBAC

Management should work from everywhere and not everyone should do everything? No problem with TLSPilot: WebUI and RBAC. A role sets who may create, change and distribute certificates, deployments and credentials - down to a single one.

Six roles: Reader, Manager, Owner, Deployment Admin, Deployer, Credential Admin.

WebUI sign-in on the management host

Own CA

TLSPilot obtains certificates automatically from public and internal certificate authorities, validates domain ownership, and gets the certificate issued straight away - without a manual step. ACME providers in every edition. Own CA from Professional.

Tenants

Several customers or companies on one host, and the estates must not mix? No problem with TLSPilot: tenants keep the inventories apart. Roles can also be granted on a tenant.

Deploy catalogue

As soon as TLSPilot has issued or renewed the certificate, it publishes it to every deployment target. That happens without agents on the target systems - only with the tools already there, and with secured credentials.

Windows

  • Certificate store
  • IIS
  • File Path (WinRM)
  • UNC
  • RDS
  • Exchange
  • AD FS
  • SQL Server
  • NPS (RADIUS)

Linux (SSH)

  • Nginx
  • Apache
  • HAProxy
  • Tomcat
  • PostgreSQL
  • MySQL/MariaDB
  • File Path (SSH)

Application Delivery (ADC)

  • NetScaler
  • F5 BIG-IP

Omnissa

  • UAG (Omnissa)

Firewall / VPN

  • Palo Alto PAN-OS
  • Palo Alto Strata Cloud Manager

Azure

  • Azure Key Vault
  • Azure App Service
  • Azure Front Door
  • Azure Application Gateway
  • Azure API Management

Entra

  • Entra Application Proxy App
  • Entra App Certificate

Google Cloud

  • Certificate Manager

Amazon Web Services

  • Certificate Manager

Custom script

  • PowerShell
  • More to come…

Certificate lifetimes

Certificate lifetimes keep getting shorter, and web browsers are starting to accept only certificates that meet these lifetimes.

  1. 5 years60 months, until 1 April 2015
  2. 39 monthsfrom 1 April 2015
  3. 825 daysfrom 1 March 2018
  4. 398 daysfrom 1 September 2020
  5. 200 dayssince 15 March 2026
  6. 100 daysfrom 15 March 2027
  7. 47 daysfrom 15 March 2029
Today

Numbers from PKI surveys

Monitoring does not mean the certificate is replaced when it expires.

91%Use more certificates than in 2021
38%Still track inventory and expiry with spreadsheets or homegrown tools
17%Already monitor certificate expiry in a monitoring tool

Source: industry surveys 2024/2025

Obtain

ACME

  • Let's Encrypt
  • ZeroSSL
  • SwissSign
  • Google Trust Services
  • SSL.com DV
  • Actalis
  • Certum SSL ACME
  • Certigna OV ACME
  • DigiCert CertCentral ACME
  • GlobalSign Atlas
  • Sectigo CaaS
  • GoDaddy SSL ACME
  • More ACME v2

Enterprise CA

  • Enterprise CA (AD CS)

Private CA

  • TLSPilot CA

Deploy

Direct deployment to many systems is built into TLSPilot. Other systems can be covered with a custom script (PowerShell).

Windows

  • Certificate store
  • IIS
  • File Path (WinRM)
  • UNC
  • RDS
  • Exchange
  • AD FS
  • SQL Server
  • NPS (RADIUS)

Linux (SSH)

  • Nginx
  • Apache
  • File Path (SSH)
  • HAProxy
  • Tomcat
  • PostgreSQL
  • MySQL/MariaDB

Application Delivery (ADC)

  • NetScaler
  • F5 BIG-IP

Omnissa

  • UAG (Omnissa)

Firewall / VPN

  • Palo Alto PAN-OS
  • Palo Alto Strata Cloud Manager

Azure

  • Azure Key Vault
  • Azure App Service
  • Azure Front Door
  • Azure Application Gateway
  • Azure API Management

Entra

  • Entra Application Proxy App
  • Entra App Certificate

Google Cloud

  • Certificate Manager

Amazon Web Services

  • Certificate Manager

Custom script

  • PowerShell
  • More to come…

Renew & distribute again

TLSPilot renews every certificate at the right time and deploys it automatically. Usually in the daily check, right away when needed.

TLSPilot
24h
Checks every 24h Renewals · Deployments
Next check
IssuedExpires

Right away when needed