
Features
Agentless certificate deployment
Agentless certificate deployment means that TLSPilot deploys each certificate from one management host to its targets and binds it there to the service, without installing an agent on the target.
One host, many targets
To deploy certificates without agents, TLSPilot connects to each target over its own interface, for example WinRM for Windows servers, SSH for Linux servers or the API of a load balancer or cloud service.
The catalogue of deployment targets covers Windows services such as IIS and Exchange, Linux web servers, NetScaler and F5, Palo Alto PAN-OS and Strata Cloud Manager as well as Azure, Google Cloud and AWS. Which targets your edition includes is shown on the editions page.
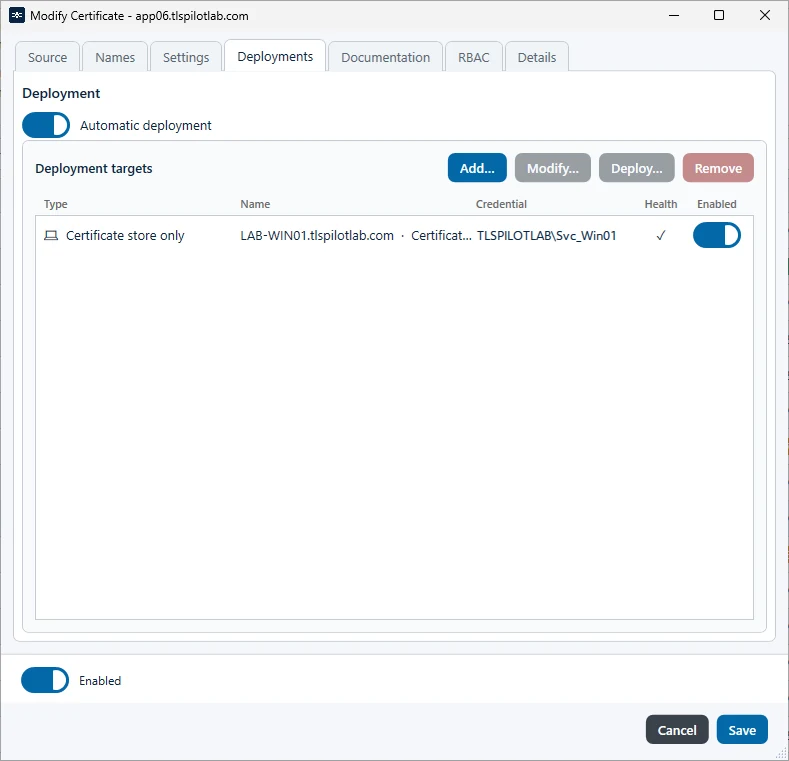
Because nothing runs on the targets, agentless certificate deployment leaves you no agent to install or keep up to date there.
Helper, deployment and health check
A Helper shows what a deployment needs, for example the permissions on the target. A deployment only counts as successful once the certificate is bound to the service. The health check then confirms that the right certificate is actually in use, in each daily cycle and after each deployment, and a dry run tests a deployment without changing the target.