
Features
Credential store integration
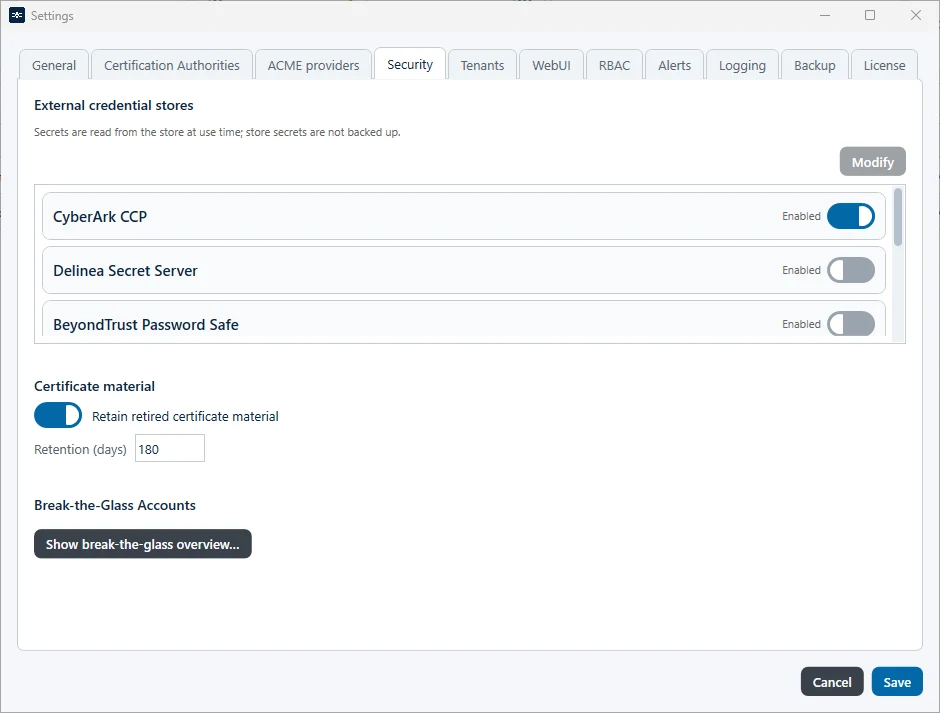
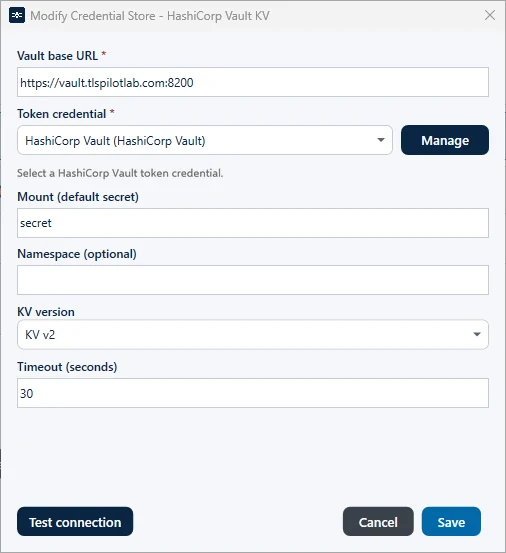
Access data for your target systems stays protected: by default TLSPilot stores it encrypted in the Windows Credential Manager of the management host. With credential store integration it takes the secret from the store you already use, such as HashiCorp Vault KV, Azure Key Vault, CyberArk, Delinea or BeyondTrust Password Safe.
Resolved at use
With an external store, TLSPilot retrieves the secret before each deployment without storing it itself. If the store rotates the password, TLSPilot therefore always uses the current one. HashiCorp Vault KV and Azure Key Vault are included from Professional, CyberArk, Delinea and BeyondTrust from Enterprise.
Managed service accounts
For Windows targets you can use a group managed or delegated managed service account instead of a user with a password. Active Directory manages its password and changes it regularly, and TLSPilot shows the PowerShell command that lets the management host retrieve it.