ACME in depth · 18.5
Multi-perspective validation
This section is background. TLSPilot cannot change how the CA validates, but the settings of your DNS, firewall and network decide whether the validation succeeds. With Multi-Perspective Issuance Corroboration (MPIC), the CA checks the challenge and the CAA records not only from its own data center, the primary network perspective, but also from several remote network perspectives in other parts of the internet. The CA only issues the certificate if enough remote perspectives see the same result. This makes it harder to obtain a certificate by redirecting traffic locally, for example with a BGP hijack. The Baseline Requirements of the CA/Browser Forum require MPIC for the ACME methods DNS-01, HTTP-01 and TLS-ALPN-01, among others.
| From | Requirement for public CAs |
|---|---|
| 15.06.2026 | At least four remote network perspectives. The confirming perspectives must be in the service regions of at least two different Regional Internet Registries (RIRs). If the quorum is not met, the CA must not issue. |
| 15.12.2026 | At least five remote network perspectives. |
Quorum: with two to five remote perspectives, one of them may disagree; with six or more, two. Perspectives count as distinct if they are at least 500 km apart, and they must not share a DNS cache. Let’s Encrypt sends five validation requests per name: one from its primary data center and four from remote perspectives. Let’s Encrypt does not publish the IP addresses it validates from, and they can change at any time.
Consequences for DNS-01
- All authoritative nameservers: Every perspective resolves the TXT record on its own and can ask any authoritative nameserver of the zone. All of them must deliver the same TXT record, including secondary nameservers that are updated later.
- Geo-DNS and traffic steering: If the DNS provider answers depending on the location of the query,
_acme-challengenames and the CAA records must have the same answer everywhere. - Split DNS: Only the public zone counts. An internal resolver, for example on the management host, can show the record although the public nameservers do not have it yet.
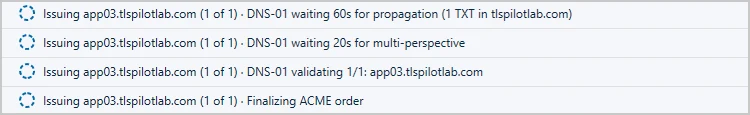
- Propagation: TLSPilot waits for DNS-01 propagation wait (seconds, 15-300), then queries the TXT record at the public resolvers of Cloudflare and Google every 5 seconds for up to about one minute until one of them sees it, and finally waits another 20 seconds, or 35 seconds if the record was not seen, before it starts the validation. The check is advisory only. If a perspective does not see the record, raise the wait.
Consequences for HTTP-01 and TLS-ALPN-01
- Geo-blocking and allowlists: The perspectives connect from different networks and countries. Geo-blocking, firewall allowlists with IP addresses of the CA or WAF rules against foreign traffic make the validation fail, even if the primary perspective succeeds. Allow port 80 or 443 from all of the internet, at least for the validation.
- Same answer everywhere: With several servers behind a load balancer or with anycast, every server that a perspective can reach must answer the challenge.
Check the nameservers
dig NS example.com +short
dig @ns1.example.net TXT _acme-challenge.www.example.com +short
Query the TXT record at every nameserver of the list. All of them must return the same value. Errors and their solutions are listed in chapters ACME, DNS-01 and HTTP-01 and TLS-ALPN-01.
Sources
- CA/Browser Forum, Ballot SC-067 v3 “Require domain validation and CAA checks to be performed from multiple Network Perspectives”, vote ended 22.07.2024: cabforum.org/2024/08/05/ballot-sc067v3-require-domain-validation-and-caa-checks-to-be-performed-from-multiple-network-perspectives-corroboration/
- CA/Browser Forum, Baseline Requirements for TLS Server Certificates, version 2.3.1, section 3.2.2.9 “Multi-Perspective Issuance Corroboration”: github.com/cabforum/servercert, docs/BR.md
- Let’s Encrypt, “Multi-Perspective Validation Improves Domain Validation Security”, 19.02.2020, and “Let’s Encrypt Continues Partnership with Princeton to Bolster Internet Security”, 30.05.2024: letsencrypt.org
- Let’s Encrypt documentation: FAQ (IP addresses for validation), Challenge Types and IPv6 Support: letsencrypt.org/docs
- RFC 8555, section 8.3 (HTTP-01 on port 80), and RFC 8737 (TLS-ALPN-01 on port 443)
While the CA validates, the status bar of TLSPilot shows each phase: the propagation wait, the wait for multi-perspective validation, the validation itself and the finalization of the order, see Figure Status bar while TLSPilot waits for propagation and multi-perspective validation.