
Product
Certificate lifecycle
The certificate lifecycle covers every step a certificate goes through, from the request to its replacement before it expires. Managing these steps is called certificate lifecycle management (CLM), and TLSPilot automates them on your own management host.
Phases of a certificate
A certificate is issued by a CA, deployed to the systems that use it and checked there. Before it expires it is renewed, and in the end it is revoked or replaced. TLSPilot tracks each certificate through all these phases and keeps a complete history.
Renewal in the lifecycle
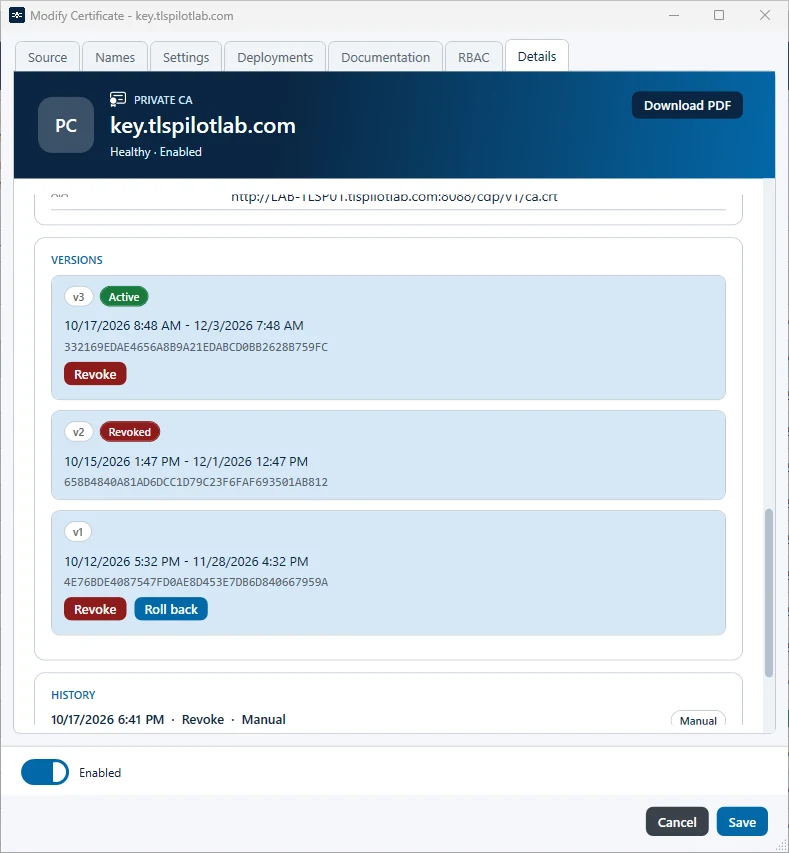
In TLSPilot renewal and deployment are separate steps. The renewal runs early in the renewal window, and the next daily cycle deploys the new certificate and checks its health. If a renewed certificate causes trouble, you can roll back to a retained previous version that is neither revoked nor expired.
This matters more every year: with public lifetimes of 47 days from 15 March 2029, a certificate would have to be renewed eight to twelve times a year.
Which software does this for you, and on which host, is described on our page about certificate management software.